Experienced security leadership, when you need it
Security needs more than policies and checklists. It needs someone who can connect security decisions to business priorities.
You get a leader who helps drive the program, not just provide advice.
Working alongside your leadership
- Define security strategy and priorities
- Build and manage your security roadmap
- Identify and manage key risks
- Establish security governance and policies
- Support compliance and certification initiatives
- Review security, technology, and vendor decisions
When security questions outgrow your team
Growing without a security leader
Your business is growing, but hiring a full-time CISO isn't yet the right investment.
Enterprise customers
Security questionnaires, due diligence, and customer requirements are becoming part of your sales process.
Certification ahead
ISO 27001, ISO 42001, or SOC 2 is on your roadmap and needs experienced leadership to drive it.
Increasing security risk
Your technology, vendors, data, and operations are becoming more complex and need stronger oversight.
Entering new markets
New customers, regulations, or markets require stronger governance and someone accountable for it.
Security leadership across your organization
Security strategy & roadmap
A security strategy aligned with your business goals, risks, and priorities, with a roadmap your board can actually follow. This is the center of the mandate; everything else hangs off it.
Risk management
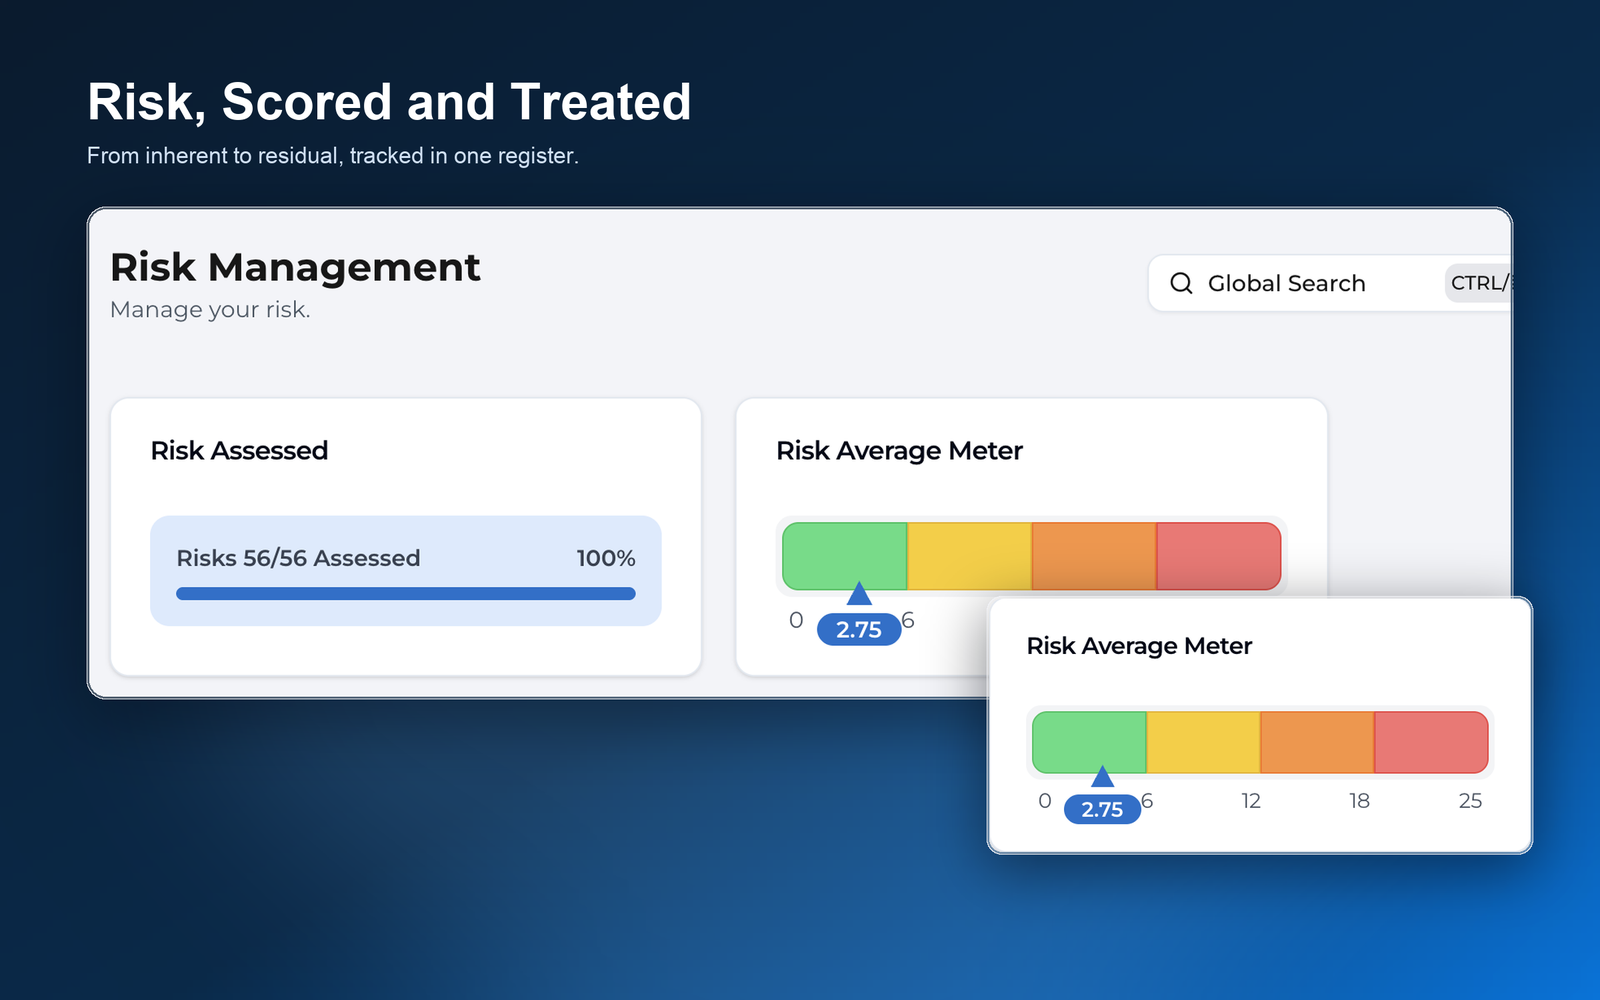
Identify, assess, prioritize, and manage the risks that matter most to your organization.
Governance & policies
Practical security policies, processes, responsibilities, and governance.
Compliance & certification
ISO 27001, ISO 42001, and SOC 2 initiatives, from preparation through ongoing management.
Security & vendor review
Oversight for technology, architecture, vendors, and key business decisions.
Incident readiness
Stronger incident response capabilities, responsibilities, and preparedness.
Executive reporting
Security risks, progress, and priorities translated into clear information for leadership, boards, and customers.
Independence by design
A vCISO is not an internal audit
A vCISO helps build, manage, and improve your security program. An internal auditor independently assesses it. When FEHA provides both, the team supporting your program never performs its independent internal audit.
Your vCISO builds it
- Builds, manages, and improves the program
- Sets strategy and owns the roadmap
- Embedded in your decisions, week to week
Your internal audit checks it
- Independent assessment of that same program
- Impartial by mandate, not by preference
- Findings your certification auditor will trust
More than vCISO
A vCISO sets direction. If you need independent assurance or hands-on testing, FEHA provides those as separate services too.
Use one or combine them
FAQ
Frequently asked questions
Everything you need to know
about our vCISO advisory.
Put a name on security
Twenty minutes is enough to scope what a vCISO engagement looks like for your company: cadence, scope, and where to start.
Need an independent audit instead?Scope your engagement
Talk directly to a certified lead. ISO 27001 Lead Auditors, CISSPs, and CISMs, the people who would work your file.
Book a consultation