FEHA is certified,
just like we help you become.
View our Trust Center
ISO 27001
Certified
ISO 42001
Certified
CSA STAR
CertifiedAdd an expert team, not just a platform.
Going it alone costs money and months.
$4.44M
Average breach cost, IBM 2025
6-12 months
To reach ISO 27001 alone
The seven steps below get most clients certified in 3-5 months.
Define your scope
Start with a clear understanding of your business, assets, processes, and compliance requirements.
Add an expert team, not just a platform.
We plan, guide, and stay even after the audit.
Going it alone costs money and months.
$4.44M
Average breach cost, IBM 2025
6-12 months
To reach ISO 27001 alone
The seven steps below get most clients certified in 3-5 months.
Define your scope
Start with a clear understanding of your business, assets, processes, and compliance requirements.
Identify gaps & risks
Assess your current posture, identify control gaps, and prioritize the risks that matter most.
Manage your frameworks
Map requirements across your chosen frameworks and manage controls, policies, and evidence in one place.
Manage vendors & access
Assess third-party risks and manage access to ensure the right people and vendors have the appropriate level of access.
Monitor employee compliance
Keep track of the compliance requirements that apply to your people, including device compliance, policy acknowledgements, and background checks.
Monitor your security
Continuously identify security weaknesses across your environment with vulnerability scanning and security monitoring.
Stay audit ready
Bring everything together so your organization can track progress, resolve outstanding issues, and stay prepared for assessment.
Continuous evidence sync
Connect your entire tech stack in 60 seconds
FEHA seamlessly connects to your cloud providers, IDPs, code repositories, and HR tools via read-only connectors to automate evidence collection with zero friction.
AWS
LiveCloud

Microsoft Azure
LiveIdentity & Access
Google Cloud (GCP)
LiveCloud
Google Workspace
LiveIdentity & Access

Okta
LiveIdentity & Access

Auth0
LiveIdentity & Access
GitHub
LiveSource Code
GitLab
LiveSource Code
Bitbucket
LiveSource Code
AWS
LiveCloud
Microsoft Azure
LiveIdentity & Access
Google Cloud (GCP)
LiveCloud
Google Workspace
LiveIdentity & Access
Okta
LiveIdentity & Access
Auth0
LiveIdentity & Access
GitHub
LiveSource Code
GitLab
LiveSource Code
Bitbucket
LiveSource Code
AWS
LiveCloud
Microsoft Azure
LiveIdentity & Access
Google Cloud (GCP)
LiveCloud
Google Workspace
LiveIdentity & Access
Okta
LiveIdentity & Access
Auth0
LiveIdentity & Access
GitHub
LiveSource Code
GitLab
LiveSource Code
Bitbucket
LiveSource Code
Jira
LiveTicketing & Projects
BambooHR
LiveHR & People
Microsoft Intune
LiveDevice Management
SecDim
UpcomingSecurity Training
Jamf
UpcomingDevice Management

Trello
UpcomingTicketing & Projects

MyHRToolkit
UpcomingHR & People

Kandji
UpcomingDevice Management
Hexnode
UpcomingDevice Management
Jira
LiveTicketing & Projects
BambooHR
LiveHR & People
Microsoft Intune
LiveDevice Management
SecDim
UpcomingSecurity Training
Jamf
UpcomingDevice Management
Trello
UpcomingTicketing & Projects
MyHRToolkit
UpcomingHR & People
Kandji
UpcomingDevice Management
Hexnode
UpcomingDevice Management
Jira
LiveTicketing & Projects
BambooHR
LiveHR & People
Microsoft Intune
LiveDevice Management
SecDim
UpcomingSecurity Training
Jamf
UpcomingDevice Management
Trello
UpcomingTicketing & Projects
MyHRToolkit
UpcomingHR & People
Kandji
UpcomingDevice Management
Hexnode
UpcomingDevice Management
Two ways to run FEHA GRC
Platform only or experts included
Platform only
Do It Yourself (DIY)
Run compliance on your own terms. Full platform access: AI evidence mapping, policy drafting, automated control testing, and every framework you need. Your team stays in the driver's seat.
- For teams with in-house security or compliance capability
- Full automation from day one
- Bring experts in anytime, no replatforming
Experts included
Do For You (DFY)
A named compliance expert runs the program with you, from first gap assessment to a passed audit. Faster, lower risk, fully guided.
- ISO 27001 Lead Auditors, CISSPs, and CISMs on your file
- Pre-audit challenge and validation
- Audit support until you pass
Start either way. Add or drop experts whenever you need. Same platform, same evidence base. See pricing
Build. Comply. Prove
The infrastructure your compliance program runs on, from first control to the trust page your customers review.
Build
Risk register & ranking
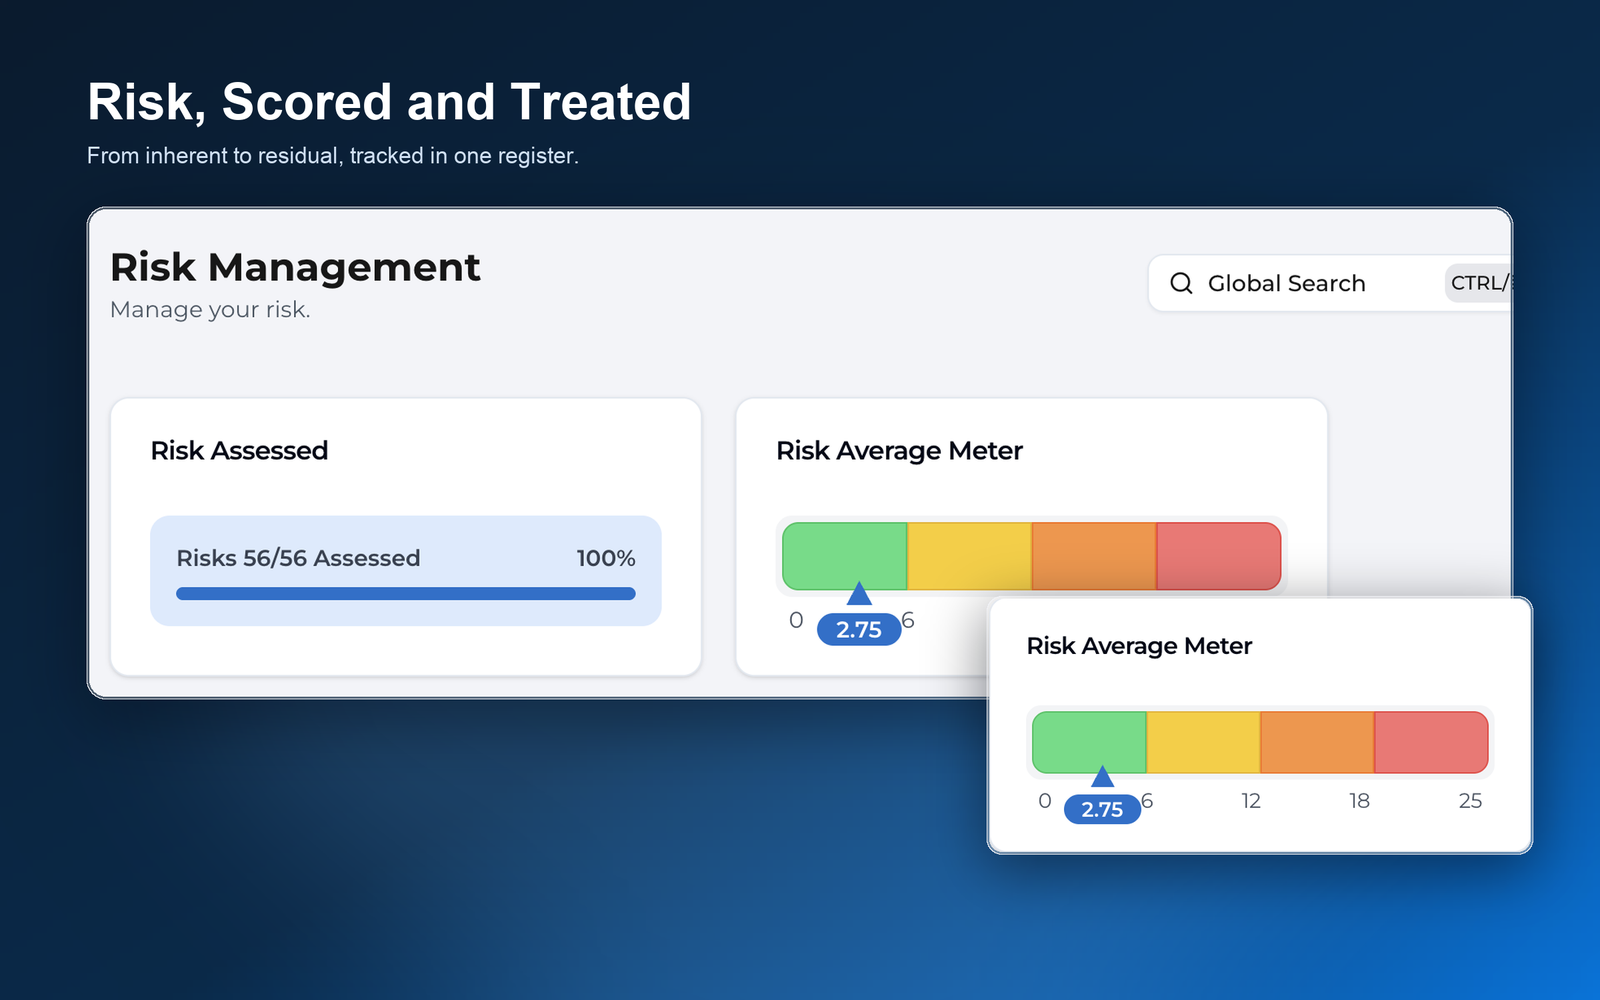
AI seeds your risk register at onboarding, scores every risk on likelihood and impact, then recommends how to treat it: accept, mitigate, transfer, or avoid. Exposure drops from inherent to residual as your team acts, tracked in one register instead of a spreadsheet.
AI-recommended risks
Your register starts populated, not blank.
Consistent scoring
Likelihood and impact scored on one shared scale across teams.
Control linkage
Mitigations map directly to controls and their evidence.
Every capability above is backed by a named compliance expert, not just a dashboard.
Wherever you operate
FEHA is more than enough!
- Global or local framework
- Startup, midmarket, or enterprise
- Finance, healthcare, AI industry, procurement, etc.
- Platform in English, Deutsch, 日本語, العربية, Bahasa Indonesia (we're adding more)
FEHA handles it all.
Don't see your country or regulations you're looking for?Talk to us
Comparison
Tools don't pass audits. The right team does
FEHA GRC runs on AI, supported by compliance experts so every gap gets caught and every fix gets done.
| Feature | FEHA GRC | Typical compliance tools |
|---|---|---|
| Platform Modules | ||
| Compliance Platform | ||
| Website Vulnerability Scanner | ? | |
| Live Simulation (no sales call) | ? | |
| Expert Support | ||
| Expert Team Available | ? | |
| Pre audit Challenge & Validation | ? | |
| Regional Coverage | ||
| Country & Regional Coverage | 33 frameworks across 12 coverage regions | ? |
| Localized Interface | EN · JP · AR · DE · ID | ? |
| 100% Audit Pass Rate | Not tracked | |
Client Reviews & Outcomes
Enterprise trust, proven by results
Due to strict confidentiality and non-disclosure agreements, client security details remain private. Verified case studies, audit outcome reports, and reference calls are shared directly upon request.
100%
Audit Pass Rate
Every FEHA client passed their certification on the first attempt.
NDA Protected
Client Confidentiality
We protect our clients' security posture and compliance disclosures with enterprise-grade privacy.
3-5 Mos
Average Certification
From initial gap analysis to audit sign-off, guided step-by-step by certified lead auditors.
Want to see our client reviews and case studies?
Connect with our team to explore anonymized audit packages, industry-specific references, and proof of 100% first-attempt passes.
Contact us for client reviewsBlog & Resources
Simplified compliance explanation
Guides, regulatory updates, and news from the field. Clear, jargon-free, and shorter than your control list.
FAQ
Questions, answered
Everything you need to know
before getting started.
Your Next Audit
Compliant. Certified. Secured.
Automate governance, risk, security, and continuous compliance. Try our live simulation without an account, or book a demo with our experts.
- No account
- No doubt
- No payment
40%
Live score